Author: Susan

  • Who is driving the digital bus?

    Who is driving the digital bus?

    This webinar is part of our Accidental IT Leaders webinar series.

    To join future webinars sign up at lumenas.com/webinar or email us at hello@lumenas.com

    Share your details to access the webinar

    In this session we covered:

    • How someone is already making your technology decisions — the question is whether it’s you, your workforce, or your IT provider (or a mix of all three)
    • How to define your organisation’s IT governance requirements, so you know your obligations and whether you’re actually owning the key calls
    • Four questions to ask your IT provider at your next meeting
    • Questions sent in from our Accidental IT leader community
  • Submission to the Inquiry into cyber security for small to medium sized businesses and organisations

    Submission to the Inquiry into cyber security for small to medium sized businesses and organisations

    Australian small and medium businesses (SMBs) are widely seen as more vulnerable to cyber security incidents and crime. To better understand the issue and find directions for new solutions, the Australian House of Representatives voted to create a Select Committee on Cyber Security for Small to Medium Sized Businesses and Organisations.

    The Chair of this committee, Sally Sitou MP, described it as the first federal inquiry to specifically examine this issue for small businesses, noting that “small businesses are on the frontline of cyber risk but too often they’re expected to defend themselves without the time, tools or resources they need.”

    This committee received bipartisan support, with the Shadow Minister for the Digital Economy, Aaron Violi MP, calling it an “important committee” and putting forward a supportive proposal for a member of the Opposition to be deputy Chair, which was accepted by the Government.

    We provided a submission to the Committee to share what we’ve learnt about this problem in our work at Lumenas, and put forward a range of proposed actions for government, the business community and industry associations to address this issue systematically. Lumenas provides one part of broader solution through our tools for accidental IT leaders, but we think there’s more work to be done across the economy so small businesses are better supported.

    To read our full submission click here.

  • Find the right AI assessment

    There are dozens of AI readiness quizzes online. Most are written for large organisations with a dedicated IT team, so a lot of the questions don’t suit a small or medium business.

    Our AI Quiz Finder sorts through them for you. We’ve collected 56 quizzes, and three short questions point you to the one that suits your situation. It takes about a minute.

    If you’re not sure where to start with AI, this is a sensible first step. To see where your IT stands today, try our IT Check as well.

    Try the AI Quiz Finder here.

  • How MS Australia uses Lumenas

    How MS Australia uses Lumenas

    “Continuously strengthening our governance and operations helps MS Australia build resilience, protect our mission and maintain the
    trust of our members and the wider MS community.”

    – Sonya Blondinau, Head of Corporate Services and Company

    Secretary, MS Australia


    How MS Australia used Lumenas to strengthen technology governance

    “Technology supports our day-to-day work in research and advocacy and helps us inform, empower and champion people affected by MS, along with their communities and loves ones.”

    MS Australia used the Lumenas IT Check to undertake an independent assessment of their technology use against best practice.

    MS Australia’s Head of Corporate Services, Sonya Blondinau describes the output from the IT Check as “a strategic, business-focused approach that made next steps easy to implement.”

    About MS Australia

    MS Australia is the largest funder of MS research in Australia and manages national research initiatives including the MS Australia Brain Bank, the MS Australia Clinical Trials Network and the Australian MS Longitudinal Study. Through the Lived Experience Expert Panel, we bring lived experience into governance, research, policy, advocacy, education and awareness, while publishing trusted information and resources that inform, empower and champion the MS community.

    Lumenas gave them greater confidence and opportunities to improve

    “While it was good to hear we already had a strong approach, Lumenas’ independent oversight gave us greater confidence in our governance of outsourced IT and technology support, while identifying focused opportunities for continuous improvement.”

    Want to learn more? Book a demo here or email us at hello@lumenas.com

  • Working with an IT Provider

    Working with an IT Provider

    For many businesses, especially those under 200 staff, your IT provider is one of your most critical vendors. They hold the keys to all of your data, and when IT stops, the business stops. Despite that, most businesses I speak to take a very light touch to managing this relationship. Often the job sits with the ‘accidental IT leader’. This is someone whose real role sits in operations or finance, but because they’re so good at keeping things running, they’ve been handed a few extras. IT is one of them.

    Usually the original agreement has expired, or it never had much detail to begin with, so it no longer reflects what the provider actually does for the business today. The monthly or quarterly check-ins stay focused on the operational. Tickets, outages, the printer on level two.

    So how do we know if we’re doing enough for the organisation when it comes to IT?

    Firstly, let’s not focus on perfect – I’ll write some more in the future about dialling in technology for your organisation. Most organisations would be well served to start with the basics; are you and your provider on the same page about what is actually happening? And are they following best practices?

    One of the reasons for the uncertainty is that IT, like law or accounting, carries a serious information asymmetry. Your provider has likely spent years learning their trade, and there’s no clear guide for you, the customer, on what good looks like. But unlike law or accounting, IT doesn’t come with strict professional standards or consumer protections to fall back on.

    So to break down some of that asymmetry, I want to share what I see in organisations where this relationship is working well, and some of the signs that things might be off track.

    What good looks like

    • You meet regularly with your account manager, or perhaps even the business owner.
    • You get the sense they understand how your business works, and how their services support it.
    • You receive written reports that show evidence of the work being done, in a form you can actually read and interpret.
    • Your agreement is detailed, current, and you’ve read it.
    • And at some point, you’ve had an independent set of eyes assess your security, or confirm the services you’re paying for are the right fit.

    Signs things might be off track

    • You can’t find a copy of the agreement at all. Or you can find it, and it’s under two pages, with no service level agreements and little detail about what the provider actually delivers.
    • No one meets regularly with the person who manages your account.
    • Your meetings are full of technical jargon, and you leave confused or frustrated.
    • And the only checks you’ve seen on security or performance have come from the provider themselves.

    None of these are reasons to panic, but they are signs to dig a little deeper.

    Take action

    We’ve built a tool that helps organisations understand what’s really happening in their IT, and whether they and their provider are on the same page. It’s called the Lumenas End-to-End IT Check. It produces a shared responsibility view showing what your provider covers, what sits with you, and where the gaps are. All in a short report you could take to your CEO or board.

    It takes one hour of your time, and not knowing the answers going in is the whole point. We’re looking for accidental IT leaders who want more clarity. Two weeks from now, you could have a clear picture of where things stand and how to move forward, in board-ready language, without needing a technology degree to read it.

    Find out more here, or email hello@lumenas.com if you’d like to speak with us about how to get more from technology in your organisation.


    This piece was originally published here on Linkedin as part of the Leading Digital series from Longitude Advisory.

  • Why are you doing the office housework?

    Why are you doing the office housework?

    I once eagerly joined a work-extra-curricular group that used data analysis to support greater diversity and inclusion. I thought this would be a great opportunity to make something more constructive than cupcakes for International Womens’ Day and make the workplace more inclusive for lots of people. I did not anticipate this would lead to me incite a small riot in the team chat only a week later.

    There were concerns about coaching assignments, I learned, in my first meeting with this work-extra-curricular group. Apparently there was a growing perception that junior women were intentionally assigned to mid-career women coaches, simply because they were women – not because the match otherwise made sense.

    I spoke up: surely this was the lesser of two evils? Of course, there was the chance this was not a good match for junior women, but mid-career women certainly had much higher coaching loads. The talent pipeline for women strongly resembled a squished triangle – how could that ratio of mid-career to junior women possibly be fair in this coaching context? At this point in the conversation, it was still perception and conjecture, so I volunteered to analyse the data.

    The data showed that I was right and had also missed the bigger problem. Mid-career women indeed had relatively more women coachees; but also relatively more male coachees. Overall, they were doing roughly double the coaching workload of their male counterparts. I dutifully copied this analysis into the internal comms channel which I’d been told was the relevant forum for feedback and discussion.

    Coaching itself is not bad, I argued back in the early eruption of indignation from my colleagues as messages began to pour in. It can be beneficial for all involved, and for many women who feel this greatly supported their career paths it makes sense to give back. My colleagues were clearly divided into two groups: those arguing I didn’t know what I was talking about and those furiously copying in links to articles about office housework.

    Office housework became better understood through a 2017 paper in the American Economic Review. The paper found that women, more often than men, receive and accept requests for tasks with ‘low promotability’.

    This highly unequal coaching workload seemed like a pretty clear example of this problem. Coaching, in this instance, was necessary but no one got rewarded or recognised for this work, much like unloading the dishwasher. But this was partly because of how coaching was often done in this organisation.

    There are some instances of coaching that are highly valuable to the coach (even if it’s unpaid). Coaches can learn new things from their younger counterparts, including those who may have different strengths or experiences. There is also significant value in building a strong network of great people you can promote and hire in the future. The extra office housework is problematic, but while evening the load, women can also be more strategic about what tasks we accept.

    There are select tasks at work that superficially meet the definition of ‘office housework’ (no one wants to do it, but they absolutely need to get done and appear to have low promotability), but are secretly strategic opportunities. IT is a good example.

    In very large organisations, this is already looked after by IT departments, CTOs and CISOs. But sometimes there can be opportunities to join employee representative groups or ad hoc projects, like figuring out how AI is useful for your area. These aren’t quite a goldmine of strategic opportunity, but they’re a pretty solid silver.

    IIn all other organisations, IT is a goldmine of strategic opportunity. If you leverage this well, you can:

    • Use it as an opportunity to write a strategy that actually gets implemented – this doesn’t have to be long or complicated, it just needs some ROI (including positive feedback) you can use in your next job interview.
    • Use it as an opener for a listening tour – by leveraging your strategy as an opening to have coffee and learn from more senior people in your field who have also been accidental IT leaders (as long as your current boss is fine with any organisational information shared as part of this tour).
    • Use it as training for managing people with skillsets that are different to yours (like your external IT vendor) – this is one of the hardest things to learn at work, and it’s also rare (but highly valuable) to get experience in this before becoming super senior.

    I’m learning that IT is frequently managed by accidental IT leaders, many of whom see it as office housework. We also know that tech is grossly underutilised in lots of small and medium organisations. Instead of telling these time-strapped small teams to get ‘smarter’ about tech, let’s empower accidental IT leaders with the right training and tools to be more strategic about managing tech for their organisation and themselves.

    At Lumenas, we’re working on making better tools for accidental IT leaders. If you’re an accidental IT leader, or you’d just like to learn more about this problem, let us know at hello@lumenas.com


    This post was originally published on Linkedin here.

  • Ice Cream Shop or Military Base?

    Ice Cream Shop or Military Base?

    Cyber security can often feel like a game of absolutes — either we’re secure or we aren’t. But it’s more complicated than that. The answer is almost always that we’re somewhere in between.

    Cyber risk, like all other risk, exists on a spectrum. We have to decide how much risk we can tolerate, then apply treatments and other mitigations to close the gap. Determining that tolerance is one of the most important technology decisions boards and executives make — it informs the whole cyber security program.

    But how do we know what our risk appetite is?

    One discussion exercise I run with organisations helps find the answer. Everyone in the room gives a number from 1 to 5 describing the organisation’s ideal cyber risk posture. One is an ice cream shop. Five is a military base.

    The purpose isn’t to land on some point in between that describes us perfectly. The purpose is to have an open conversation about the kinds of risks we face, the ways we use technology, and how much tolerance the business has for disruption.

    Take the ice cream shop. We’re probably taking digital payments and using some systems for ordering ingredients and managing staff, but we aren’t storing sensitive customer data. If we go offline, we can keep operating on cash, or take payments from a backup mobile terminal. Cyber hygiene still matters, but security may not be a major area of investment. Even at the low end the basics are non-negotiable — the scale starts from one because no one is at zero.

    Now think about the military base. Security is top of mind. We’re storing extremely sensitive information, and we need assurance that it hasn’t been accessed without authorisation or altered. The success of our information systems can be a matter of life and death — we rely on them for far more than information storage, from accessing controlled stores to communicating time-sensitive orders and managing access by identity and clearance. Here there’s serious investment in a layered security program that is continuously monitored, reviewed, and improved.

    Most of the organisations I work with land somewhere in the middle. The exercise gives us a group conversation that can challenge assumptions and build a consensus on what our ideal posture looks like. Usually we start with a few different positions in the room — some say three, some say five — and over the course of the discussion we work out why those positions were chosen. I’m yet to work with a group that couldn’t reach a consensus to carry forward into the decisions that follow.

    From there, I most organisations benefit from formalising the output of that discussion in a risk appetite statement. That can be used alongside governance activities like reviewing cyber risk assessments, developing treatment plans, or shaping an organisational cyber security program. As leaders, we can direct investment more confidently and understand the trade-offs we’re making with risk because we’ve had a clear conversation about what it actually means for our organisation.


     This article was originally published here on Linkedin as part of the Leading Digital series from Longitude Advisory.

  • Stories from the basement: how fictional IT leaders shape our perception of IT leadership

    Stories from the basement: how fictional IT leaders shape our perception of IT leadership

    Early in building Lumenas, we found ourselves often reading job advertisements for IT Managers. Not because we were hiring, but because job ads are a frank assessment of what an organisation thinks a role involves. This helps us better understand the misunderstanding of IT roles, and how persistent these issues may be, which helps us better design our products which help close this gap. 

    Looking at job ads helped us check whether anecdotal experiences were more systematic. Do organisations persistently misunderstand what IT leaders do? We expected this would probably be the case, but we were struck by the consistency.

    The most consistent gap we noticed was the near-total absence of governance. The technical requirements were detailed, but the leadership and management expectations were vague. Based on the job descriptions we looked at, you would expect people in these roles to be tactically proficient, highly responsive but rarely proactive. 

    We know this isn’t an accurate depiction of what IT leadership requires, or looks like, in reality. This gap in the perception and reality of IT leadership is probably shaped by a number of factors. One factor that seemed worth better understanding was the role of pop culture.

    Pop culture significantly shapes our perceptions of careers. Perhaps most famously, the release of the original Top Gun move inspired a nearly 10% increase in US Navy recruitment. The portrayal of particular occupations shapes our expectations about jobs and the people in them.

    To better understand how Western pop culture has shaped our perceptions of IT careers we decided to start a weekly series in which we’d analyse iconic IT characters.

    Six weeks, six characters, five questions

    We spent six weeks analysing fictional IT managers to better understand how pop culture portrays the role and how those portrayals might be shaping the expectations of the people who hire, manage, and work alongside IT leaders.

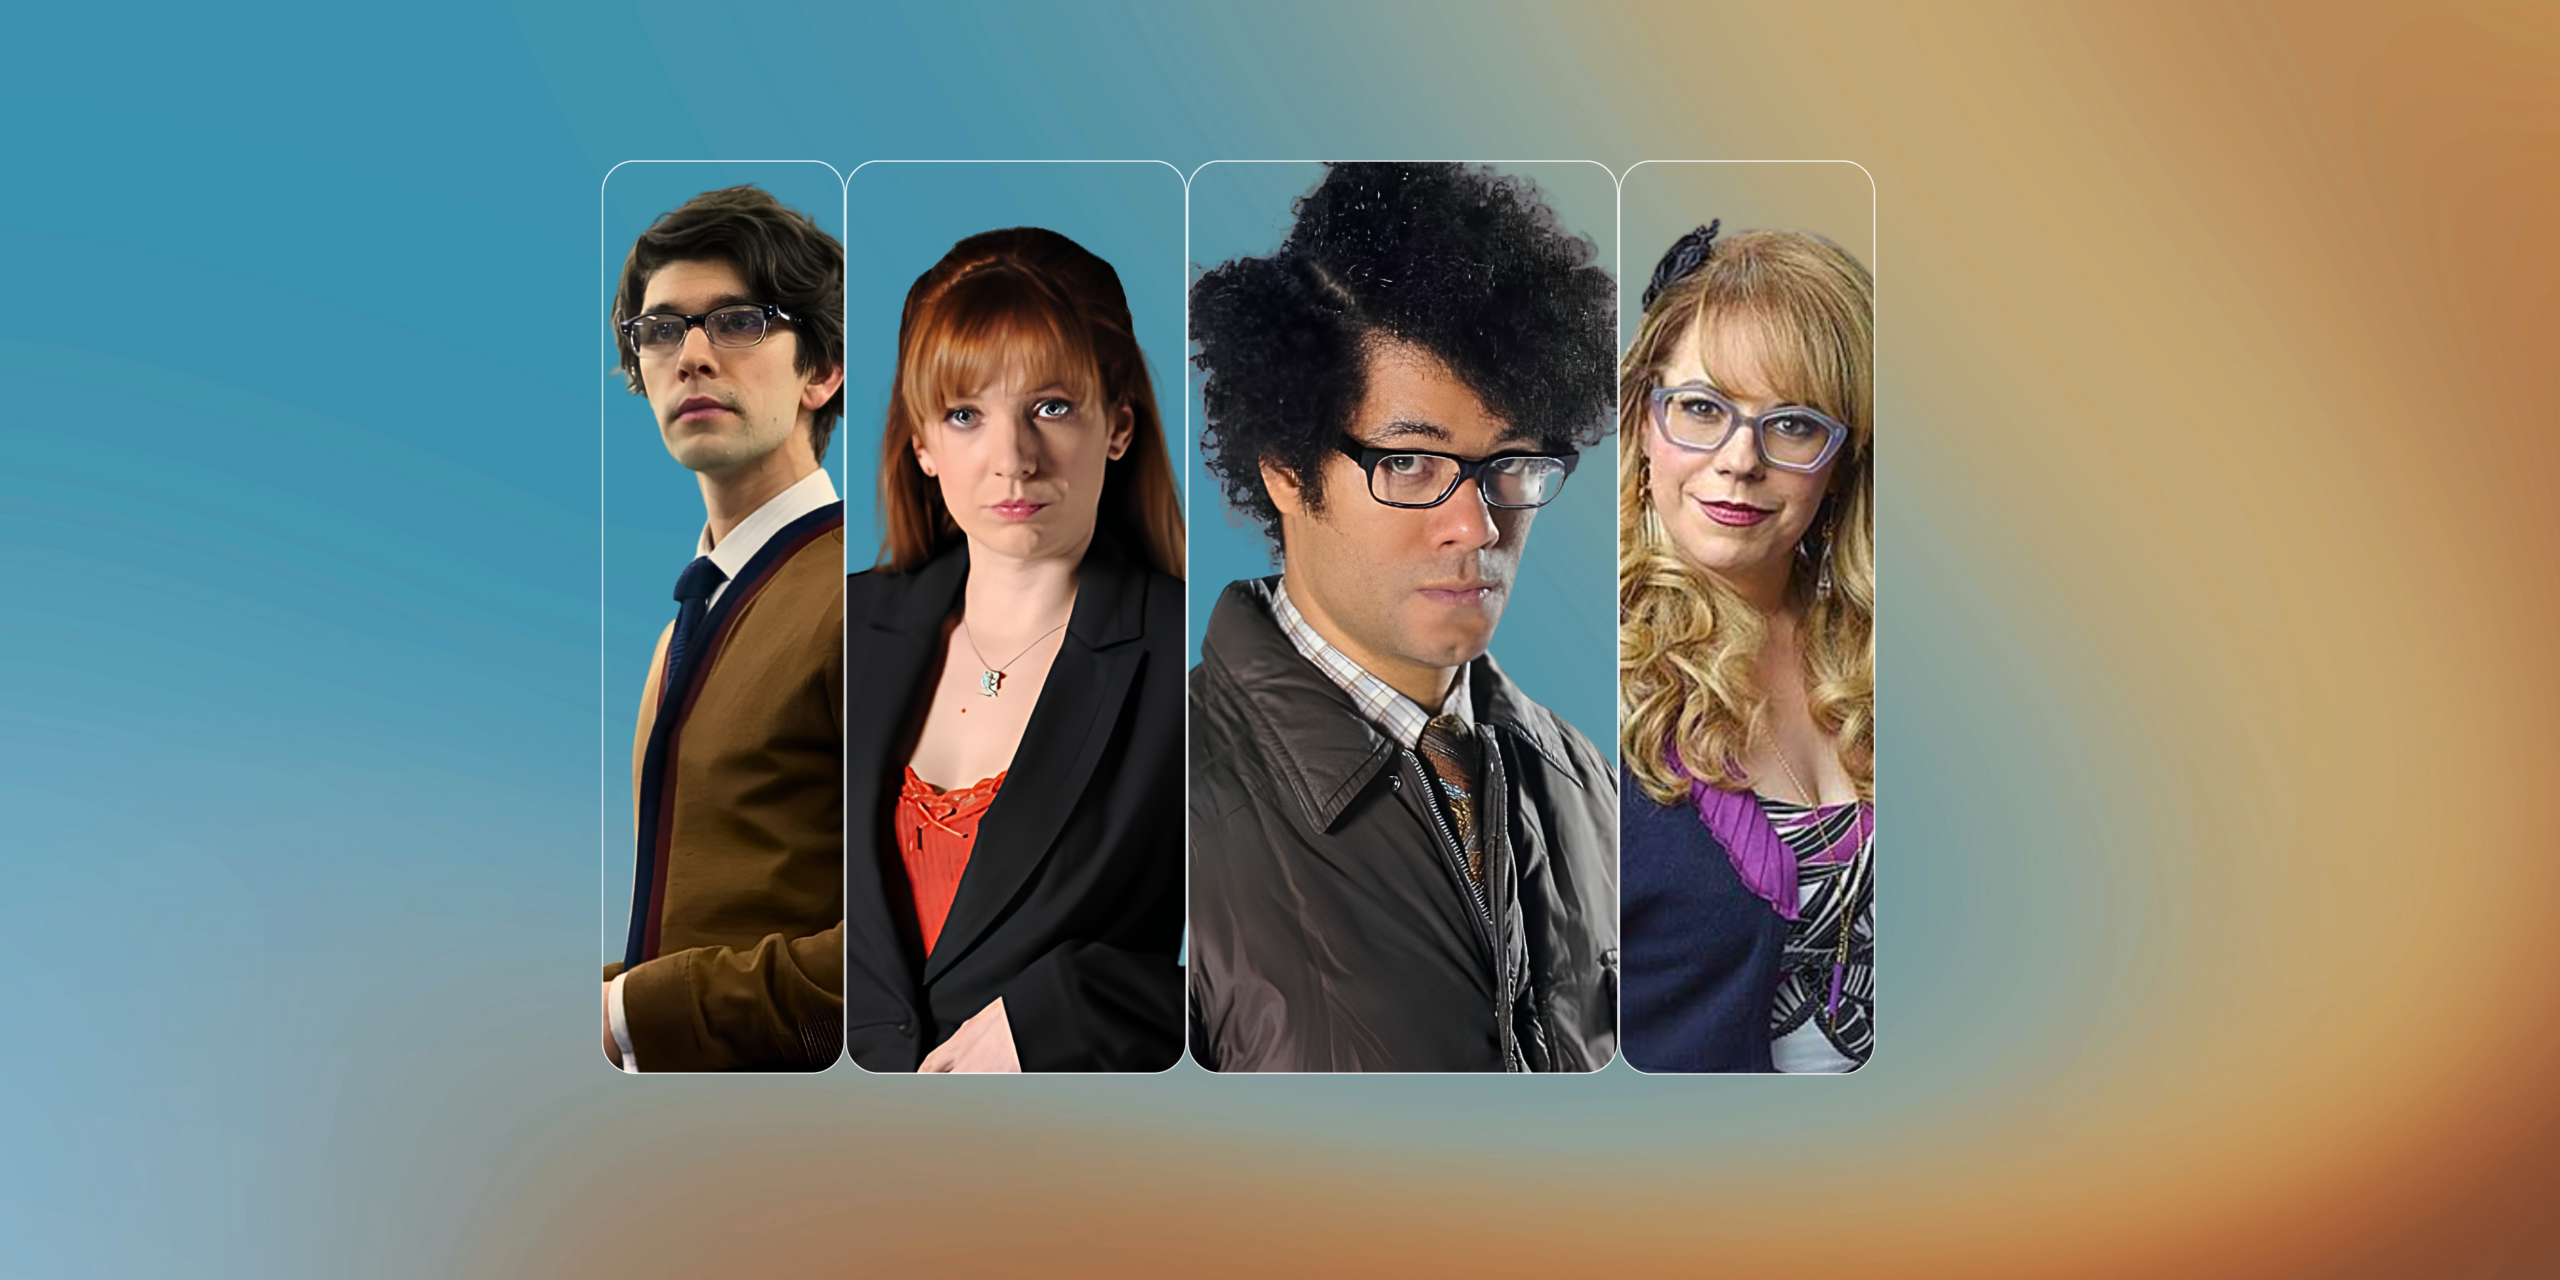
    We chose six characters: Moss and Jen from The IT Crowd, Gilfoyle from Silicon Valley, Abby from NCIS, Penelope Garcia from Criminal Minds, and Q from the James Bond franchise. We asked the same five questions of each character.

    Is this character a punchline or a person? We wanted to know whether the show treated its IT character as a fully realised human being, or as a recurring joke. The distinction matters: a character who exists to be laughed at teaches the audience something different about IT than one who is shown to have depth, growth, and genuine relationships.

    Is this a realistic portrayal of IT leadership? Not technically accurate (we weren’t looking for accurate depictions of network architecture) but realistic in terms of what IT leadership actually involves. Does the character deal with stakeholders? Manage ambiguity? Operate under constraints? Or does technology simply work like magic whenever the plot requires it?

    What cultural value does this place on IT? Is IT work portrayed as cool, respected, and consequential? Or as something slightly embarrassing; tolerated rather than valued? This question gets at the status the show implicitly assigns to the role.

    How mature is this character’s IT leadership? Are they reactive – fixing things when they break – or are they building systems, developing people, and shaping the direction of their organisation? We scored this on a spectrum from firefighting to force-multiplying.

    How likely are they to adopt Lumenas? We included this partly for marketing purposes but also because it forced us to think concretely about each character’s relationship with management tools. If presented with a tool that would require you to actively opt into thinking strategically about the business of IT, would you welcome it? Or shun it?

    Asking the same five questions across six characters gave us a simple basis for comparison, and pushed us to think about each character in more depth than we had as fans. This helped us learn a few things upon observation and even more upon reflection.

    What we learned

    The Peter Pan problem

    Almost every fictional IT character is frozen in time.

    Moss never learns to navigate the world outside his server room. Penelope delivers results at impossible speed across fifteen seasons but never builds a team or a system that could outlast her. Abby is the most competent person in the building, but the show never gives her adequate resources or support. Gilfoyle refuses to manage anyone and is rewarded for it. Q equips Bond and disappears. Jen tries to grow and is consistently humiliated for the attempt.

    In fiction, IT characters don’t grow up. The comedy, the drama, the narrative tension; it all depends on them staying exactly as they are.

    We called this the Peter Pan problem.

    The parent-child paradox

    There’s a second pattern that runs alongside the first, and it’s a weird twist.

    These characters are simultaneously infantilised and expected to parent everyone around them. They’re treated as oddities — socially awkward, professionally misunderstood, never quite taken seriously. But they are also the person everyone calls when something goes wrong. They’re there to fix it. Without complaint or explanation. They rarely ask for more time, resources or even information.

    The message, repeated across decades of television, is that IT leaders will always be there to save us. Not just because they’re capable — but because that’s ‘who’ they are. 

    That’s an impossible bar. No one can always give. And when the expectation is that IT leaders exist to absorb problems without limit, the question that never gets asked is: what do they need to succeed?

    Who came out on top

    When we scored the six characters across the first four questions — leaving aside the Lumenas adoption question — Q scored highest. He’s the most realistic portrayal, the most force-multiplying, and the only character in the series who is consistently treated as a peer rather than a curiosity.

    Remove question 5 on Lumenas adoption and Gilfoyle wins. He’s the most accurate portrayal of what real infrastructure work looks like, and the show respects him for it.

    Moss scored lowest by a significant margin. Almost every question landed him at the bottom of the scale. But we also learnt from our posts on Linkedin that Moss is the People’s Choice with the most likes of any character. Looking beyond likes, to see who had the highest engagement, we found that Penelope and Jen tied as the most intriguing of IT characters. More than half of everyone who saw those posts clicked through to read more.

    The contrast between the highest score and most likes taught us something important about the IT community. Technical excellence earns admiration, but genuine effort and good intent earns different kind of trust. No one thinks Moss is a good example of IT leadership, but we love him anyway. It’s hard to think of another profession where capability is so highly valued but honest effort is wholeheartedly prized.


    We hope you enjoyed this series as much as we did. It changed how we think about the gap between what IT leaders are expected to be and what they’re given to work with in most jobs.